It treats false alarms as a safety problem too.
A detector that catches scams but repeatedly frightens people about legitimate bank or payment messages is also failing.
MEDIA / PRESS ROOM
Scam Ba ’To? helps Filipinos examine suspicious messages before they click, pay, or share information—without automatically treating every OTP, bill, or security alert as a scam.
THE STORY
Scam messages increasingly borrow the language of normal digital life: OTPs, account alerts, tuition balances, bills, delivery notices, government transactions, and merchant payments.
Scam Ba ’To? was built around a simple distinction: what a message says is not the same as what it asks you to do. The checker looks at claimed identity, requested action, transaction context, destination, behavioral warning signs, and verified organization information before producing guidance.
WHY REPORTERS MAY CARE
A detector that catches scams but repeatedly frightens people about legitimate bank or payment messages is also failing.
Receiving an OTP for something you initiated is different from being told to surrender that OTP through a link, chat, or caller.
When verified information is available, the result can show independently researched official destinations rather than sending users back to the link in the message.
Controlled benchmark executions are explicitly not presented as independent real-world scam reports.
CURRENT PROJECT SNAPSHOT
Selected figures from the current public intelligence build.
Benchmark note. The project’s 48,000 controlled benchmark executions are validation cases, not 48,000 independent scam reports. The benchmark includes 16,447 exact-unique messages and 6,144 behavioral representatives. There are currently 94 source-grounded representative cases.
ONE EXAMPLE
If the user initiated the payment and the details match, an OTP can be an expected part of the transaction. The risk changes when someone asks the user to send, disclose, or enter that OTP through an unrelated destination.
This distinction is central to the project’s decision logic.
QUOTABLE
“Hindi dapat matakot ang isang tao dahil lang may OTP o malaking halaga sa text. Ang tanong ay kung ano ang nangyari, ano ang pinapagawa sa iyo, at saan ka dinadala.”
“Catching scam messages is only half the problem. If a system repeatedly scares people about legitimate transactions, it is also failing.”
“Hindi namin gustong sabihing ‘scam’ lang. Gusto naming ipakita kung bakit.”
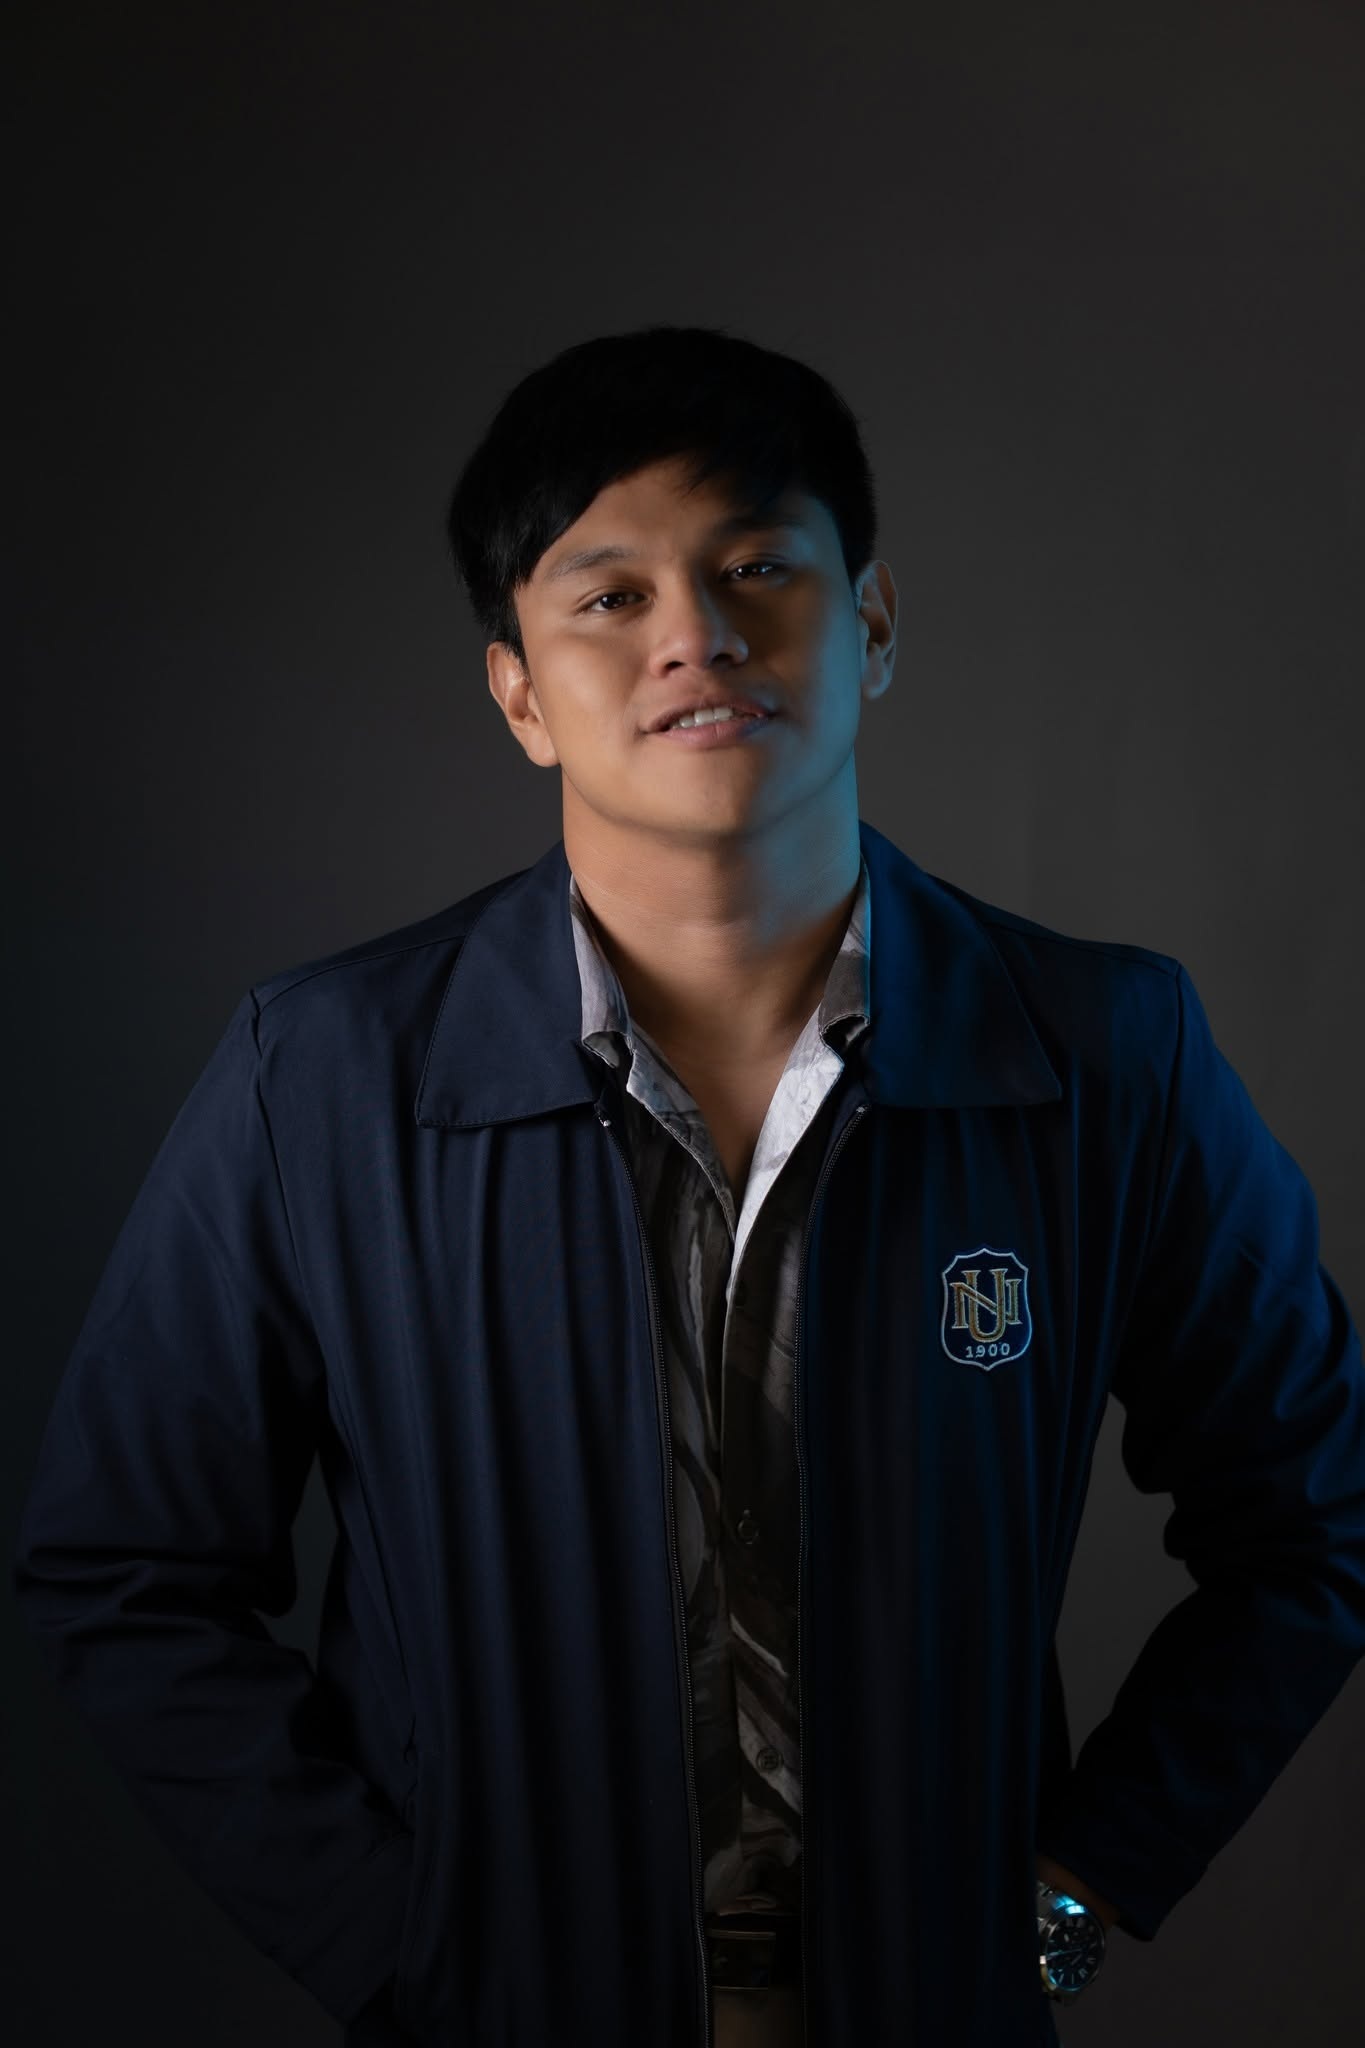
— John Clement S. Escobañez, MSIT · Developer & Project Lead
THE DEVELOPER
John Clement S. Escobañez is an information technology educator, researcher, and developer based in the Philippines. He developed Scam Ba ’To? as an independent public-interest technology project focused on explainable scam-risk guidance for everyday digital messages.
He is affiliated with the College of Computing and Information Technologies of National University - Manila.
Academic affiliation is provided for biographical identification and does not imply institutional endorsement, ownership, or responsibility for Scam Ba ’To? unless separately stated by the University.
jsescobanez@national-u.edu.ph →FOR TECHNICAL / DATA REPORTING
The public Technical Report documents the decision pipeline, Bronze–Silver–Gold data lineage, organization intelligence, benchmark construction, adversarial testing, and known limitations.
OPEN TECHNICAL REPORT →